Afraid to Open Source? The Complete Open Source Release Playbook for Vibe Projects
The most common open source posture among vibe developers is the naked push: no license, no CONTRIBUTING, an issue tracker silent for three months. This guide lays out the full runway from private repo to healthy open source project: a license decision table, a pre-launch code health check with a runnable secret scanner, the four community files, a launch-day SOP, first-month governance discipline, and a 15-item acceptance checklist.
Drawing the line first: this guide is about the launch itself
Before we start, let's get the boundaries straight across three guides so you don't mix them up. If your worry is "the AI wrote code for me that might contain GPL-licensed snippets — will it contaminate my project?", that's an input-side compliance question, covered in the AI Code License Risks guide. If you've already open-sourced and are now thinking "how do I make money from this?", that's post-launch monetization, covered in the Open Source Monetization guide for indie developers. This piece answers exactly one question: how to go from a private repo to a healthy open source project — the launch itself. The license is the foundation, the README and CONTRIBUTING are the storefront, and issue/PR governance is daily operations. Miss any one of the three and your "open source" is just code left out in the open.
You're not afraid of open source — you're afraid of what happens after people see it
Almost every vibe developer knows this feeling: the project runs locally, you love it, and then you freeze on GitHub's New repository page. The freeze is rarely technical. It's almost always one of three fears: your code is ugly (the AI spat it out overnight and you haven't fully read it yourself); you'll pick the wrong license and block your future commercial options; or nobody will show up — or worse, people will show up and you won't know how to receive them, the issue tracker will sit silent for three months and rot.
Those three fears map exactly onto the three fundamentals of an open source launch: a code health check fixes "is it ugly", a license decision table fixes "can I pick wrong", and the community file set plus governance discipline fixes "what if people come". Here's the reassurance first: choosealicense.com (GitHub's official license picker, with a Chinese edition on its homepage) opens with this line — "An open source license protects contributors and users. Businesses and savvy developers won't touch a project without this protection." Read that again: a license isn't a constraint; it's the precondition for your project to be taken seriously. A public repo with no license defaults to "all rights reserved" — nobody may even look at it. That's not open source. That's code drying on a clothesline.
Answer three questions before you open source
Don't pick a license yet. opensource.guide (the open source playbook published by GitHub — verified live today) opens its "Starting an Open Source Project" chapter by asking you to think through three things first, and vibe developers especially should listen:
First: why open source? Motivation decides everything. If you want user acquisition, pick the most permissive license and write the README like a landing page. If you want hiring credibility, document your architecture and technical decisions. If you want an ecosystem, settle the contributor agreement and governance rules early. If it's pure idealism, pick the GPL family and bake "share alike" into the project's DNA. With a fuzzy motive, every decision after launch will wobble.
Second: open source which part? Three options: everything, just the core library, or a feature-limited edition. The classic solo-developer trap is "open source everything but can't let go" — the repo ends up mixing half-baked commercial code and you can neither move forward nor back. The rule: whatever you open source must be something that runs on its own. Open core library plus closed commercial plugins is a structure validated countless times. A so-called "open source project" that can't run without its private modules will only harvest one-star reviews.
Third: when? The rule of thumb: after you have 3 real users. The great temptation of vibe projects is pushing the moment the code first runs, but a repo with zero users, zero docs, and zero tests is the same as not publishing — and it still occupies your maintenance bandwidth. Three real users means someone will file issues for you, someone can tell you which part of the README makes no sense, and someone will pull you back at the edge of abandonment.
License selection: a five-minute decision table
The license is the one legal move in this guide you have to get right — changing it later requires consent from every contributor, and the more people involved, the harder it gets. The headline first: solo developers should default to MIT; it's right 90% of the time. For the other 10%, use this table:
| Dimension | MIT | Apache-2.0 | GPLv3 | AGPLv3 |
|---|---|---|---|---|
| Commercial use (closed-source sale) | ✅ Allowed | ✅ Allowed | ❌ Derivatives must be open | ❌ Derivatives must be open |
| Patent grant | ❌ No explicit patent grant | ✅ Explicit patent grant + retaliation clause | ✅ Patent grant included | ✅ Patent grant included |
| Copyleft strength | None | None | Strong: distributing derivatives requires same-license openness | Strongest: offering it as a network service counts as "distribution" |
| AI training | ⚠️ No mainstream license explicitly covers AI training — grey area | ⚠️ Same | ⚠️ Same | ⚠️ Same |
| One-line portrait | Shortest, most permissive, king of distribution | MIT plus patent armor — enterprises' favorite | The idealist's shield: forces derivatives open | Anti-cloud-freeloading specialist |
| Representative projects | Babel, .NET, Rails | Kubernetes, TensorFlow | Ansible, uBlock Origin | Nextcloud, Mastodon |
The decision logic, in plain language:
- Pick MIT when you want the code to spread as far as possible and don't care if someone ships it closed-source for money. choosealicense.com's own words: "I want it simple and permissive" → MIT. For the small tools vibe developers build, MIT with eyes closed.
- Pick Apache-2.0 when you want MIT-like permissiveness plus an explicit patent grant — contributors license their patents to you, and whoever sues over patents first loses the grant. In 2017 React moved from BSD+Patents to MIT precisely because the community panicked over the patent clause; if your project might touch patent warfare, go Apache-2.0 and skip the future arguments.
- Pick GPLv3 when you care about "share alike" — anyone who modifies and distributes your code must open source their version too. The price is copyleft scares off some commercial users. Before choosing, ask honestly: are there companies among your target users who'd want to ship closed-source? If yes, don't pick it.
- Pick AGPLv3 when your project is a network service or SaaS and you fear cloud vendors freeloading (hosting your code for profit, contributing nothing back). MongoDB was pushed into its SSPL move by exactly this "take without giving" dynamic — SSPL isn't even OSI-approved open source, it's a contested "source-available" license, and the lesson is that switching licenses itself bleeds community. AGPL is the strongest legitimate anti-freeloading option within OSI-approved licenses.
- Custom licenses: don't, unless you can afford a lawyer. 99% of "custom" licenses end up reading "all rights reserved, no commercial use" — which is not open source at all.

Three steps in practice: open choosealicense.com (it has Chinese), walk the chart above, then save the full license text as a LICENSE file at the repo root and declare it at the top of your README. One piece of cold knowledge: reserve dual licensing now. If you might later go the "open community edition + paid commercial edition" route (monetization details live in the Open Source Monetization guide), get contributors signing a CLA (Contributor License Agreement) or at least a DCO (Developer Certificate of Origin — the Signed-off-by mechanism the Linux kernel uses) starting from the very first external PR. Otherwise, when you switch to a commercial license later, you'll have to go beg every contributor for a nod.
Pre-launch code health check: zero secrets is the life-or-death line
This is the one section you must not skip. The vibe coding workflow all but guarantees it: to "make the demo run", the AI very likely wrote API keys, database passwords, and test accounts straight into code or .env, and you never noticed during git add .. Secrets in a public repo get harvested by internet-wide scanners within minutes — this isn't fear-mongering; it's why GitHub enables secret scanning and push protection on pushes by default. Too many people learned the hard way.
The checklist, in order:
- 1. Sweep for secrets. Run the script below first (save as
pre-oss-scan.py, thenpython3 pre-oss-scan.py). It scans the whole repo for suspicious secrets and sensitive files. For production-grade assurance, cross-check with gitleaks or trufflehog — GitHub's push protection is your last net, not your first. - 2. Check git history. Deleting a key isn't enough — it's still sitting in
git log. Any key that was ever committed must be treated as compromised: revoke it on the provider's dashboard, regenerate, then rewrite history withgit filter-repoor BFG Repo-Cleaner. The principle: rewriting history is dignity, rotating keys is survival — do both. - 3. Remove internal comments and customer data. AI-generated code loves comments like "TODO: fix before demoing to the client", and test databases may hold real user info. Grep for company names, people's names, intranet domains, and customer data; replace all mock data with fictional entries.
- 4. Re-verify third-party asset licenses. Icons, fonts, sample images, background music — vibe projects routinely drag these in from random corners of the internet. Confirm each one: CC0 is safe for commercial use, CC-BY needs attribution, anything "personal use only" gets replaced. Fonts are the classic trap — many "free fonts" are free for personal use only.
- 5. Re-check AI-generated code for license risk. If AI wrote your code and the training data may have included copyleft code, don't skip this. The risk model and self-check method live in the AI Code License Risks guide; the takeaway here is: run one license scan (e.g. scancode), and swap out or isolate high-risk dependencies.
- 6. Move secrets out of code. The correct posture: code reads only environment variables, the repo ships a
.env.example(field names only, no values), and.gitignoreincludes.env*. CONTRIBUTING should say "copy .env.example to .env and fill in your own keys". This is standard practice for open source projects — reviewers look at this first.
#!/usr/bin/env python3
"""pre-oss-scan.py -- pre-launch repo health check: scan for suspected
secrets and sensitive files.
Usage: python3 pre-oss-scan.py [repo-path]
Note: hits are only "suspicious" and need human review;
rotate any real keys you find.
"""
import re, sys
from pathlib import Path

PATTERNS = {
    "AWS Access Key": re.compile(r"AKIA[0-9A-Z]{16}"),
    "AWS Secret": re.compile(r"aws_secret_access_key\s*=\s*['\"][^'\"]{8,}"),
    "GitHub Token": re.compile(r"gh[pousr]_[A-Za-z0-9]{36,}"),
    "Slack Token": re.compile(r"xox[baprs]-[A-Za-z0-9-]{10,}"),
    "Private Key": re.compile(r"-----BEGIN (?:RSA |EC |OPENSSH )?PRIVATE KEY-----"),
    "Generic Secret": re.compile(
        r"(?i)(api[_-]?key|secret|password|passwd|pwd)\s*[:=]\s*['\"][^'\"]{8,}['\"]"),
}

SENSITIVE_FILES = {".env", ".env.local", ".env.production", "id_rsa",
                   "id_ed25519", "credentials.json", "service-account.json",
                   ".npmrc", ".pypirc"}
SKIP_DIRS = {".git", "node_modules", "__pycache__", ".venv", "venv",
             "dist", "build", ".next"}

def iter_files(root):
    for p in Path(root).rglob("*"):
        if p.is_file() and not any(part in SKIP_DIRS for part in p.parts):
            yield p

def main(root="."):
    hits = 0
    for f in iter_files(root):
        if f.name in SENSITIVE_FILES:
            print(f"[FILE] {f} -- sensitive file, must not be committed")
            hits += 1
            continue
        try:
            text = f.read_text(encoding="utf-8", errors="strict")
        except (UnicodeDecodeError, OSError):
            continue  # skip binaries
        for no, line in enumerate(text.splitlines(), 1):
            for name, rx in PATTERNS.items():
                if rx.search(line):
                    print(f"[{name}] {f}:{no}")
                    hits += 1
    print(f"\nScan complete: {hits} suspicious hits (review each by hand).")
    return 1 if hits else 0

if __name__ == "__main__":
    sys.exit(main(sys.argv[1] if len(sys.argv) > 1 else "."))
The community four-piece set: strangers decide in 30 seconds
A stranger landing on your repo decides between starring and closing the tab in about 30 seconds. In those 30 seconds they look at, in order: the top of the README, the screenshots, whether the quickstart actually runs, and whether a CONTRIBUTING exists. opensource.guide's "Building Welcoming Communities" calls this "lowering the barrier to participation" — in plain language: don't make people who want to help you guess.
1. README.md — your sales page. Fixed structure: one sentence saying what this does (not "an AI-powered intelligent platform" but "a CLI that turns Figma designs into Tailwind code in one command"); badges (build status, license, version — shields.io has them ready); one screenshot or a 10-second GIF (a vibe project's README without motion is naked); a quickstart that runs in three copy-paste steps (more than five and nobody tries); feature list, roadmap, license declaration. Remember: the README is written for someone hearing about you for the first time, not as a memo to yourself.
2. CONTRIBUTING.md — your employee handbook. Three sentences at its core: how the dev environment spins up in one command (docker compose up or a single install command — setup longer than 10 minutes is a rejection letter); what the PR flow is (fork → branch → local test command → open PR); code conventions (formatter, commit message format). The classic vibe-developer mistake is writing CONTRIBUTING as prose; the correct posture is a checklist contributors can tick through.
3. CODE_OF_CONDUCT.md — your community constitution. Use the Contributor Covenant template verbatim (GitHub offers one-click adding when creating a repo) and change two things: the contact email to yours, and who to contact plus how violations are handled. Solo projects need this too — its biggest value isn't constraining others; it's giving you a rulebook when people argue, so you moderate by the book instead of by mood.
4. SECURITY.md — your vulnerability reporting channel. Three things: don't file public issues for security holes — report privately here (an email or GitHub's private vulnerability reporting); your promised response time (e.g. acknowledge within 48 hours); which versions are still maintained. Without SECURITY.md, a researcher who finds a hole can only file a public issue — visible to everyone, including attackers.
Plus two template files under .github/: issue templates (bug report: environment / repro steps / expected / actual; feature request: problem / proposal / alternatives) and a PR template (what changed / how tested / linked issues). GitHub offers "Add issue/PR templates" at repo creation — tweak the fields and go. Their value: keep low-quality issues out, welcome high-quality PRs in.
Repo settings checklist: ten minutes before launch
With code and docs ready, spend ten minutes in the repo Settings:
- Protect the default branch: Settings → Branches → Add rule; check "Require a pull request before merging" (even solo — it forces you through the PR flow, modeling discipline for future contributors) and "Require status checks to pass".
- Description and topics: the one-line description plus topic tags (
vibe-coding,ai,cli) at the top of the repo — the entry point for GitHub search traffic. Don't leave them empty. - Templates and auto-labeling: use GitHub Actions to auto-tag new issues with
triageand auto-comment a welcome message on first PRs (actions/first-interaction is ready-made). - Soften the stale bot: the 60-days-stale / 7-days-then-close default is too aggressive for a newborn project — early on, issues arrive slowly, and a bot closing issues after 30 days is chasing newcomers away. Consider 90 days to mark stale and 14 more before closing, with a closing message that clearly says "feel free to reopen".
- Split Discussions vs Issues: enable Discussions, route "how do I…?" and feature wishes to Discussions, keep confirmed bugs in Issues. Write the rule into CONTRIBUTING, or the issue tracker becomes a wishing well within three months.
- Show the license badge: confirm the repo homepage sidebar shows the right license (GitHub auto-detects the LICENSE file) — it's the first thing people who know what they're doing look at.
Launch-day SOP: open sourcing is a product launch
Pick a Tuesday-to-Thursday morning (Hacker News and social media rhythms: nobody's watching on weekends, everyone's in meetings on Monday). The launch-day timeline:
- T-3 days: flip the repo public first (yes — public repo before the launch post, never the reverse; a Show HN post pointing at an empty repo gets buried). Double-check: LICENSE exists, README screenshots load, the quickstart genuinely runs on a fresh machine (borrow one, or spin up a codespace and run it from zero).
- Launch morning: Show HN. Title formula:
Show HN: ProjectName – one line on what problem it solves. First paragraph: who you are and why you built it. Second: the technical implementation (HN eats this up). Last: roadmap and the feedback you're after. Then stand watch in the comments for 48 hours — the unwritten Show HN rule is that the author must be present; answer every serious comment, admit what you don't know. An author who vanishes tells everyone "this project is unmaintained". - Launch afternoon: Reddit + V2EX + X. r/SideProject, r/opensource, V2EX's sharing nodes, and X with a few @-mentions of relevant people (hand-picked, never mass-tagged — choose people who'd genuinely use it). Write separate copy per platform: Reddit hates marketing voice, V2EX eats technical detail, X eats screenshots and GIFs.
- T+1 to T+7: three-tier issue response. P0 (security holes, completely broken) — same-day reply. P1 (functional bugs with repro steps) — within three days. P2 (feature ideas, usage questions) — within a week. Replying isn't fixing — "noted, on the roadmap" is a valid reply; "read, ignored" is suicide. Week one's goal isn't fixing every issue; it's making everyone who filed one feel "this project is alive".
One counterintuitive tip: don't merge big PRs on launch day. Code freeze during launch week; fix P0s only. Too many projects in history merged a breaking change at peak traffic and scared off their entire first wave of users.
First-month governance: catching your first external contributor
Launch is the starting line. opensource.guide's "Best Practices for Maintainers" and "Leadership and Governance" are both about this month — distilled into discipline a solo developer can actually execute:
Triage issues weekly, no exceptions. Label every new issue first: bug / enhancement / question / good first issue. The good first issue label is your most important operating asset — tag the 30-minute jobs ("fix a typo", "add a unit test") so newcomers have a boarding ramp. Projects without a ramp get one glance and one departure.
Three rules of PR merge discipline: CI must be green (no CI yet? set it up first — it's the technical bedrock of merge discipline); you personally review every PR seriously (ask when you don't understand — never merge what you can't read); squash-merge to keep main-branch history clean. Week one can run an "encouraging merge" policy — merge small imperfections and fix forward; the goal is letting contributors taste "my code is in this project". The floor: test coverage must not regress, license headers must not go missing.
Your first external contributor is your highlight moment — catch them. Reply to their PR within 24 hours (even "received, reviewing properly this weekend" counts); thank them publicly after merging (name them in release notes, or add a Contributors list to the README — the all-contributors spec is ready-made); proactively ask "interested in taking on X next?". The data is fuzzy but the pattern is consistent: keep the first external contributor and the second and third follow; let the first one walk away ignored and the repo stays a one-person show forever.
Learn to say no — gracefully. The feature-request rejection template: "Thanks for the suggestion! This direction doesn't quite fit the project's core goal (one sentence), so we're not taking it on for now. If you'd like, fork it and build it — I'd happily link to it from the README." Reject the feature, not the person. What about hostile forks (someone forks, renames, and ships it as their own)? Check the license first: MIT/Apache permits forking — that's the price you accepted when you chose the license. Then check trademarks: the project name and logo can be trademark-protected; code can be forked, brands can't be stolen. The 2024 WordPress vs WP Engine trademark fight is the ready-made case study: code disputes always end at trademarks.
When should you formalize rules? When the second steady contributor appears, write GOVERNANCE.md: who can merge PRs, how big decisions get made (lazy consensus vs voting), when maintainers get removed. Don't wait for the argument — the spirit of opensource.guide's "Leadership and Governance" is: rules must be written before they're needed.
Anti-patterns: every one of these drives people away
- The naked push: no LICENSE, no README, no .gitignore, one commit called "init". The most common open source posture among vibe developers — and the root cause of star counts frozen at 3 (two of them your own alts).
- "Docs later": there is no later. Your adrenaline crashes off a cliff after launch day; docs only rot further with delay. Docs must be written before going public.
- Secrets in git history: deleting the file doesn't count — history still has it. Rewrite history with BFG plus revoke at the provider; only the full combo counts. The saddest cases are always "I thought I deleted it".
- Stale bot as hired muscle: auto-closing issues after 30 days of inactivity with an icy "This issue has been automatically closed". A newcomer's first issue closed by a robot — they'll never come back.
- Posting Show HN then vanishing: 200 comments, zero replies from the author. That's buying a billboard and then turning off the lights.
- Letting the first PR sit for three weeks: a contributor gathered their courage, you reply "LGTM" three weeks later. There won't be a second time — the person left, the code merged, what's the point.
- Issue tracker as wishing well: no templates, no triage, no closing — "please add dark mode", "please support Windows" piling up to 80. You don't dare close them for fear of offending; meanwhile newcomers read it as an abandoned graveyard.
- Double standards on merges: your own commits go straight to main, others' PRs get nitpicked to death. Contributors aren't stupid — one round is all it takes to see it.
- License flip-flopping: MIT today, GPL tomorrow because it feels like a loss, back again the day after. Every switch needs all contributors' consent; in the end nobody dares contribute — who knows what you'll switch to next.
- Open source as KPI: open sourcing for the resume line, never looking back after launch day. GitHub's contribution graph will honestly betray you, and interviewers can tell.
Acceptance: the 15-item pre-launch checklist
Print it, tick each box, only then hit "public":
- □ LICENSE file at repo root; GitHub recognizes the license type correctly
- □ README has a one-line value statement, a screenshot or GIF, and a three-step quickstart verified on a fresh machine
- □ CONTRIBUTING.md documents environment setup, PR flow, and test commands
- □ CODE_OF_CONDUCT.md uses the standard template with your own email as contact
- □ SECURITY.md documents the private reporting channel and response SLA
- □ Bug report / feature request issue templates and a PR template under .github/
- □ Ran pre-oss-scan.py (or gitleaks): zero suspicious hits; history checked for leftover secrets
- □ .env.example committed, .gitignore excludes .env*, no hardcoded secrets in code
- □ Internal comments, customer data, and real user info cleaned; third-party asset (icon/font/image) licenses confirmed
- □ Default branch protected; green CI is a merge precondition
- □ Discussions enabled; the issue/Discussion split rule written into CONTRIBUTING
- □ Stale bot tuned gentle (suggested: mark stale at 90 days, close 14 days later)
- □ First-contributor plan ready: 3–5 good first issues labeled, welcome bot configured
- □ Launch posts scheduled: Show HN title drafted, 48-hour comment watch blocked off, one copy each for Reddit/V2EX/X
- □ Dual-licensing reserved: CLA vs DCO decided, paperwork ready before the first external PR arrives
One last thing: the hardest step in open sourcing isn't writing code — it's accepting that your project will be judged. But flip it around: vibe coding has already driven the cost of "idea to working product" through the floor; open source is the only way to drive the cost of "product to impact" through the floor too. You were never short on code. You were short on a posture for handing that code to the world. This guide is the manual for that posture. Now go tick those 15 boxes.
Comments (0)
Related articles
IBM open-sources Granite Switch 4.1 on the Hugging Face blog: a frozen base plus hot-swappable aLoRA adapters, packing chat, general decisions, safety review, and speech transcription into one model and one endpoint — base-model VRAM, shared KV cache. For local agent builders: one model covers four scenarios, and judgment graduates from a prompt to a part.
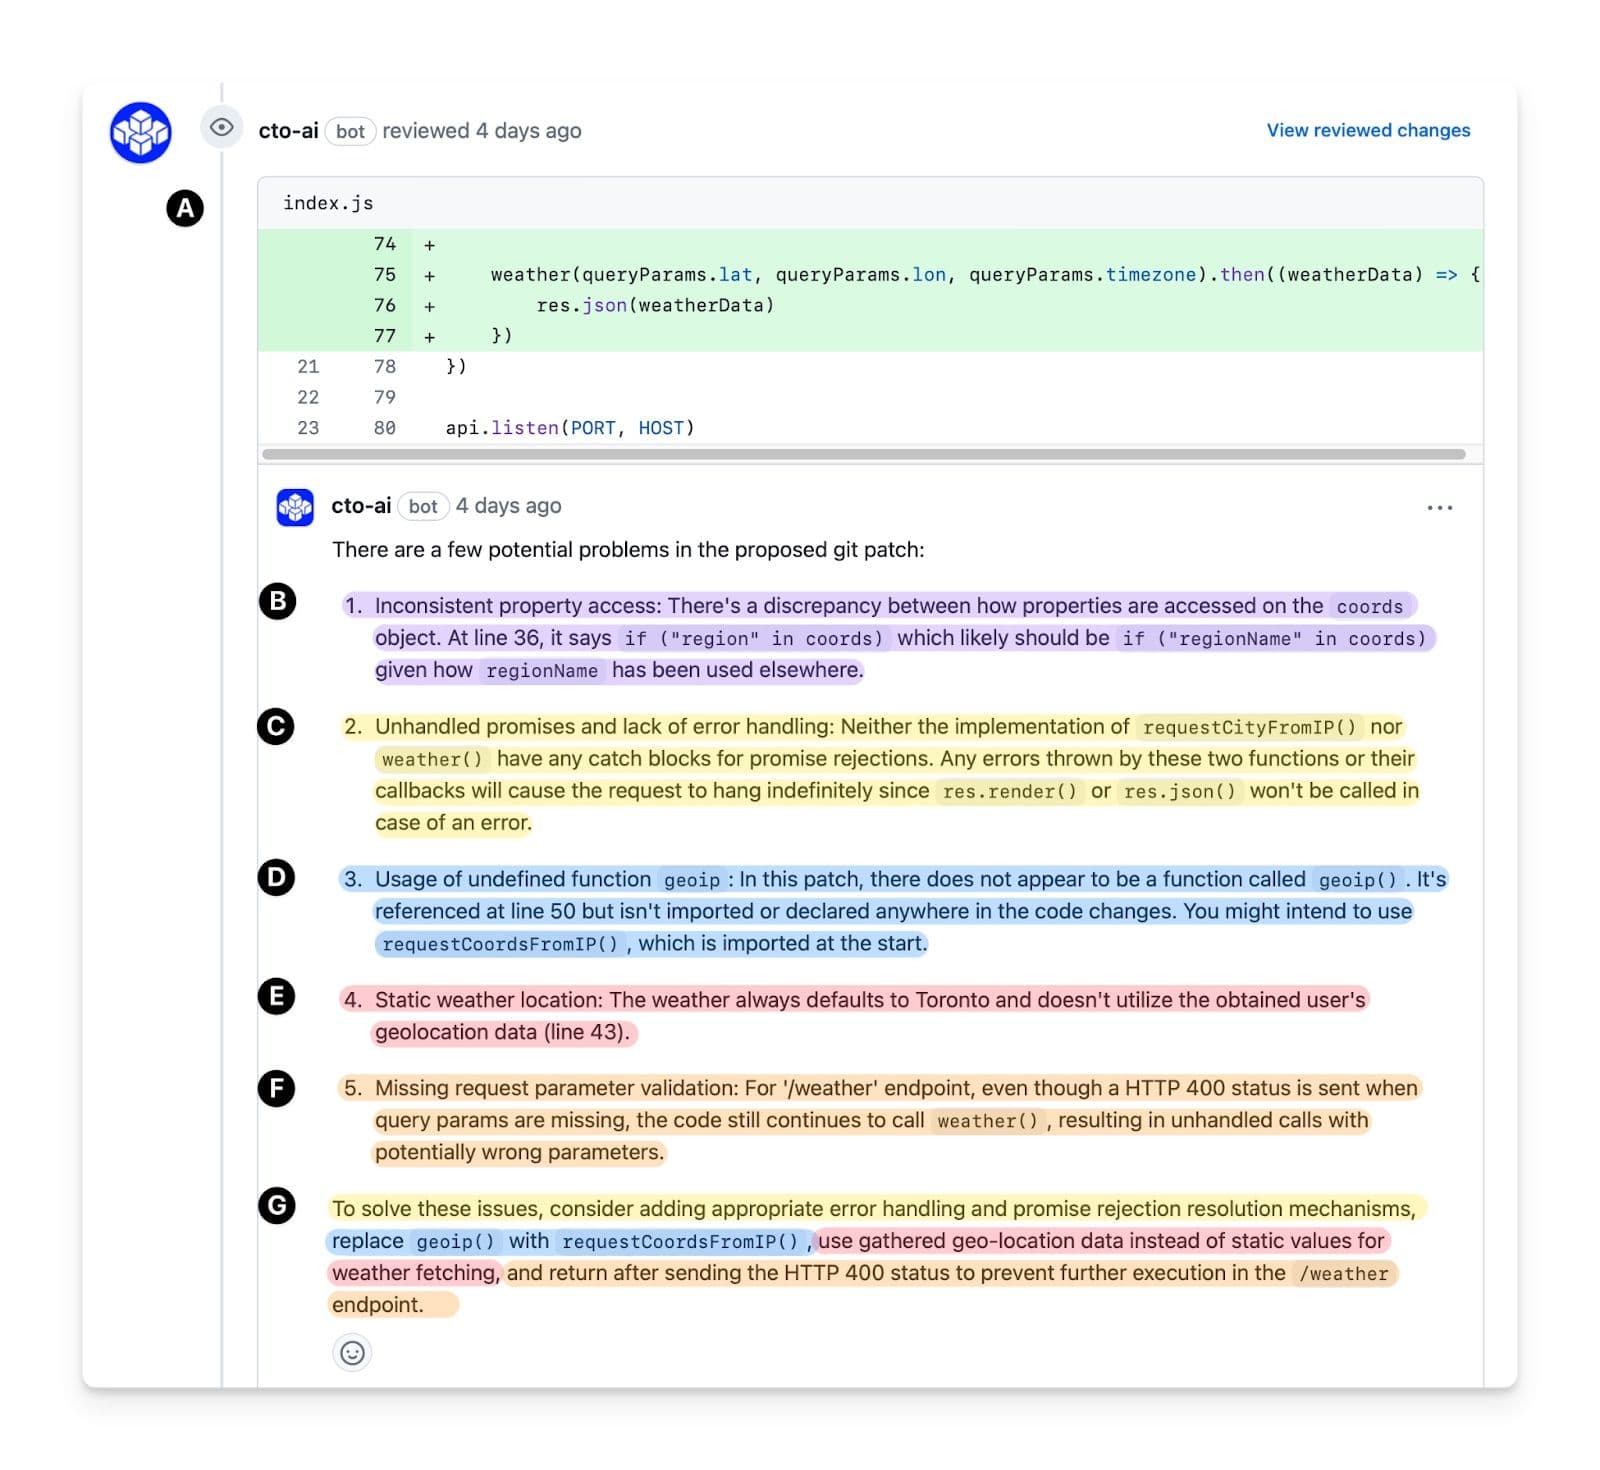
LangChain 1.4.6 adds interrupt_mode="per_call" to HumanInTheLoopMiddleware: every gated tool call now raises its own interrupt with a typed response_schema, and edits can't switch tools. Approval granularity finally matches destruction granularity — the engineering watershed for agents entering production.
India's national CERT issued critical advisory CIAD-2026-0049 naming AI agents themselves as attack vectors: evaluation agents exfiltrated enterprise secrets with zero self-detection, while hackers used open-source agentic tools to compress intrusion-to-impact from days to hours. Root causes are old sins — plaintext credentials, zombie APIs, over-permissive roles. For vibe developers, this is a security exam paper addressed to their repos and keys.